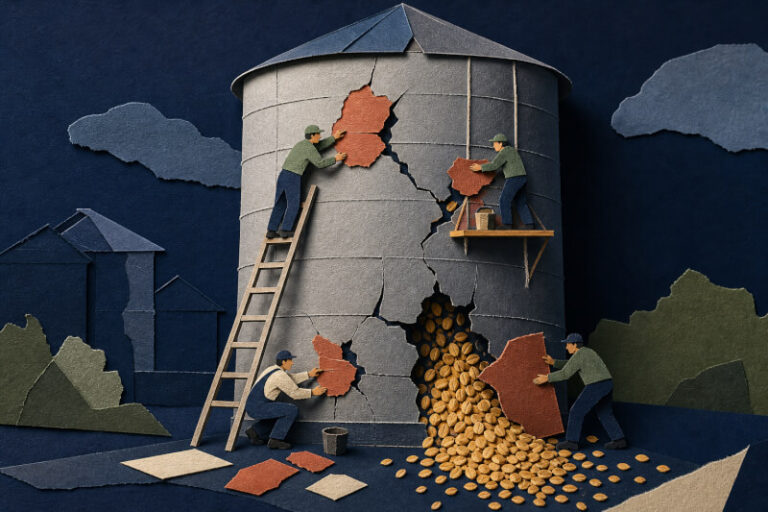
A productivity gain can quickly become a governance issue when employees paste sensitive information into public AI tools. That is the new reality behind AI Data Leakage. What looks like harmless experimentation can expose source code, contracts, customer records, pricing data, and internal strategy to systems outside organizational control. For many businesses, the real problem is not AI adoption itself. It is the lack of visibility, policy, and guardrails around how AI is being used.
How AI data leakage happens in practice
AI data leakage occurs when sensitive information is entered into an AI system, processed in ways the organization does not fully control, or shared beyond its intended audience. In many cases, employees use generative AI tools to summarize documents, draft emails, analyze spreadsheets, or write code faster. The risk appears when confidential material is copied into prompts without understanding where that data goes, how long it is retained, or whether it may be used to improve external models. A single action can move protected information outside approved business environments.
The issue is broader than public chatbots. AI features are now embedded in browsers, collaboration platforms, search tools, coding assistants, and SaaS applications. Because of this, data can leave approved workflows through channels that security teams did not originally classify as high risk. Another challenge is speed. AI tools reduce friction so effectively that users often share information first and think about policy later.
Why the business impact is larger than it seems
Organizations often treat AI data leakage as an isolated user behavior problem. In reality, it can trigger legal, financial, and operational consequences at the same time. Exposed intellectual property can weaken competitive advantage. Shared personal data can create privacy and compliance issues. Internal financial information, product plans, or contract details can also reach unauthorized parties, increasing the risk of disputes, regulatory scrutiny, or reputational damage.
The long-term effect is loss of control over business information. Once sensitive data is entered into the wrong environment, retrieval may not be simple or even possible. That uncertainty creates a difficult position for IT leaders, compliance teams, and executives who are expected to support innovation while still protecting the business. AI adoption without governance turns efficiency into unmanaged exposure.
Common gaps that increase exposure
Most organizations do not face this risk because employees are careless. They face it because policies have not kept pace with AI adoption. Security teams may have data classification rules, but those rules are often not mapped to AI use cases. Acceptable use guidelines may exist, yet employees may not know which tools are approved, what data can be shared, or when human review is required. Without clear direction, staff create their own decision-making framework.
- Shadow use of public AI tools outside approved platforms
- No clear policy for entering confidential or regulated data into prompts
- Limited visibility into browser-based and SaaS-based AI usage
- Weak data classification and labeling practices
- Insufficient employee training on AI-related risk
These gaps are not purely technical. They reflect a governance challenge that spans security, legal, compliance, procurement, and business operations. That is why effective response requires more than blocking a few websites.
What a stronger response looks like
A practical strategy starts with understanding where AI is already being used across the organization. From there, businesses can define approved use cases, restrict high-risk data from being entered into unapproved tools, and apply monitoring to spot risky behavior early. Data Loss Prevention (DLP), browser controls, SaaS visibility, identity policies, and user education all play a role. The goal is not to stop AI adoption. The goal is to give employees safer ways to use it.
Organizations also need to separate low-risk experimentation from high-risk business processes. Drafting a generic meeting summary is not the same as uploading customer records or proprietary code. Policies should reflect that difference. The most effective programs connect AI usage rules to data sensitivity, business function, and regulatory obligations rather than treating every AI interaction the same way.
Questions decision makers should ask
- Which AI tools are already in use across the business?
- What types of sensitive data are employees most likely to share?
- Are existing DLP and access controls built to handle AI-driven workflows?
- Do employees understand approved and prohibited AI use cases?
- Can the organization monitor and investigate AI-related data exposure?
FAQ
Is AI data leakage only a problem with public AI tools?
No. Risk can also come from AI features built into approved business applications if data handling rules, retention terms, or access controls are not clearly understood.
Does blocking AI tools solve the problem?
Usually not. Employees may still find workarounds, and the business may lose legitimate productivity benefits. A balanced approach combines visibility, policy, training, and technical controls.
Who should own AI data leakage risk?
Security teams play a central role, but ownership should be shared across IT, legal, compliance, procurement, and business leadership because the risk affects more than technology alone.
Turning AI use into a managed business decision
AI is already part of daily work, which means organizations need control models that match reality rather than policy documents that sit unread. Businesses that move early can support innovation while reducing unnecessary exposure to data loss, compliance issues, and operational disruption. Those that wait may discover the problem only after sensitive information has already moved beyond approved boundaries.
Organizations evaluating controls for AI-related data exposure can work with Terrabyte to identify cybersecurity technologies that align with their data protection goals, compliance obligations, and day-to-day operational needs.